Official Bank 0/129

NSE 6 – Network Security 7.6 Support Engineer (FCSS_NST_SE-7.6) - Fortinet Exam Questions

Last updated on July 22, 2026

97% Exam Compliance
129 Total Questions
1
Question
Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate.

Which action will FortiGate take when using the default settings for SSL certificate inspection?
Options
A FortiGate uses the SNI from the user's web browser.
B FortiGate uses the first entry listed in the SAN field in the server certificate.
C FortiGate uses the CN information from the Subject field in the server certificate.
D FortiGate closes the connection because this represents an invalid SSL/TLS configuration.
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

2
Question
Which two statements about an auxiliary session ate true? (Choose two.)
Select 2
Options
A With the auxiliary session selling disabled, only auxiliary sessions are offloaded.
B With the auxiliary session setting enabled. Iwo sessions are created in case of routing change.
C With the auxiliary session setting disabled, for each traffic path. FortiGate uses the same auxiliary session.
D With the auxiliary session setting enabled. ECMP traffic is accelerated to the NP6 processor.
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

3
Question
Exhibit.

Refer to the exhibit, which shows two entries that were generated in the FSSO collector agent logs.

What three conclusions can you draw from these log entries? {Choose three.)
Select 3
Options
A A firewall is blocking traffic to port 139 and 445.
B Remote registry is not running on the workstation.
C The FortiGate firmware version is not compatible with that of the collector agent.
D DNS resolution is unable to resolve the workstation name.
E The user's status shows as "not verified" in the collector agent.
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

4
Question
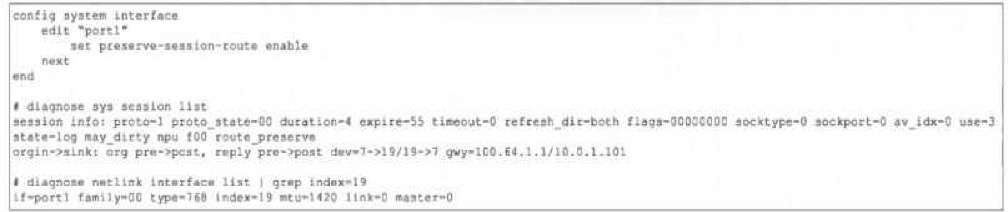
Refer to the exhibit, which shows the port1 interface configuration on FortiGate and partial session information for ICMP traffic.

Exhibit

What happens to the session information if a routing change occurs that affects this session?
Options
A Only the interface and gateway information for dev=7 will be removed.
B Sessions involving port7 or port19 will not have their routing information flushed.
C The session will be flagged as dirty but no route lookups will be performed.
D The session information will not change unless the current route has been removed from the routing table.
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

5
Question
Exhibit.

Refer to the exhibit, which shows the output of a diagnose command.

What can you conclude about the debug output in this scenario?
Options
A The first server provided to FortiGate when it performed a DNS query looking for a list of rating servers, was 121.111.236.179.
B FortiGate used 64.26.151.37 as the initial server to validate its contract.
C Servers with a negative TZ value are less preferred for rating requests.
D There is a natural correlation between the value in the FortiGuard-requests field and the value in the Weight field.
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

Finish Practice?

Are you sure you want to finish? This will end your practice session.