Official Bank 0/48

Palo Alto XDR Engineer (Palo Alto XDR Engineer) - PaloAlto Networks Exam Questions

Last updated on July 22, 2026
97% Exam Compliance
48 Total Questions
1
Question
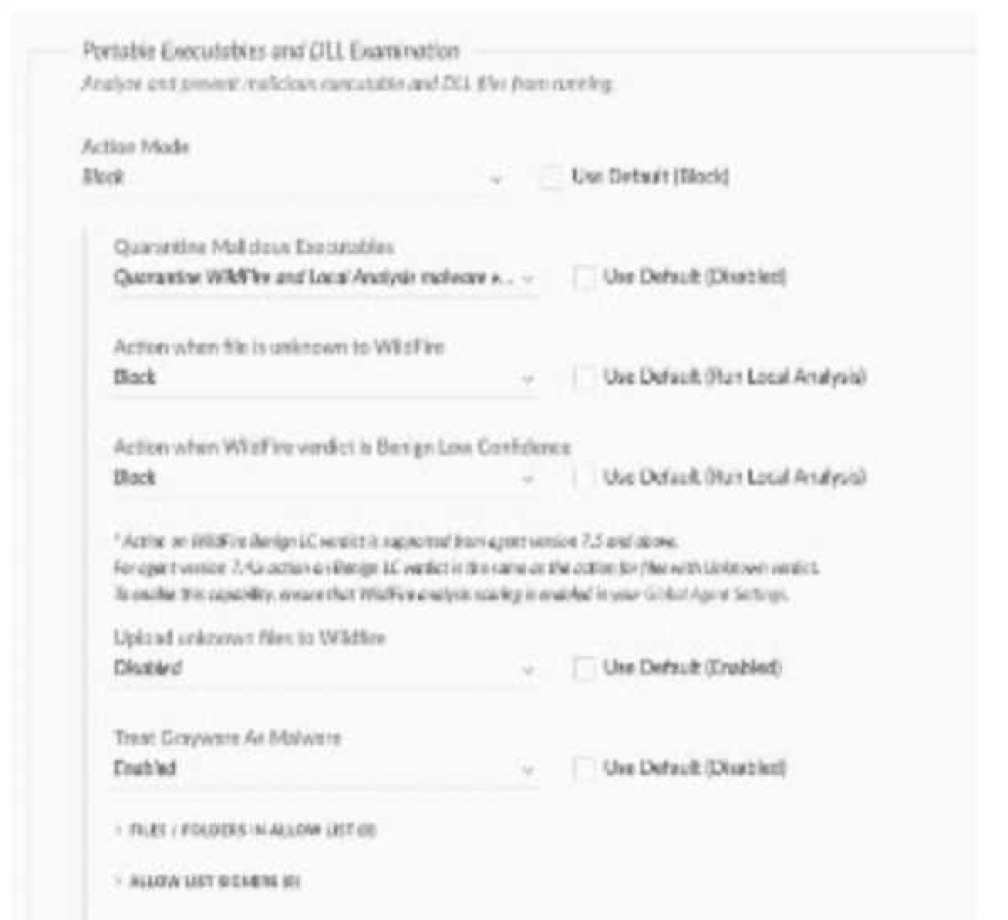
[Cortex XDR Agent Configuration] Based on the Malware profile image below, what happens when a new custom-developed application attempts to execute on an endpoint?

Exhibit
Options
A It will execute after one hour
B It will not execute
C It will execute after the second attempt
D It will immediately execute
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

2
Question
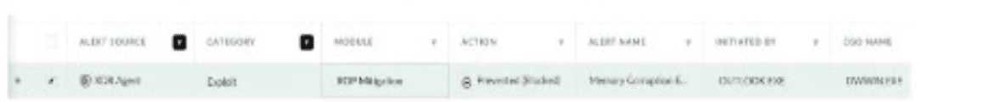
[Detection Engineering] Based on the image of a validated false positive alert below, which action is recommended for

Exhibit

resolution?
Options
A Create an exception for the CGO DWWIN.EXE for ROP Mitigation Module
B Create an exception for OUTLOOK.EXE for ROP Mitigation Module
C Disable an action to the CGO Process DWWIN.EXE
D Create an alert exclusion for OUTLOOK.EXE
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

3
Question
[Data Ingestion and Integration]

What should be configured in Cortex XDR to integrate asset data from Microsoft Azure for better visibility and incident investigation?
Options
A Azure Network Watcher
B Microsoft 365
C Cloud Identity Engine
D Cloud Inventory
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

4
Question
[Cortex XDR Agent Configuration]

How are dynamic endpoint groups created and managed in Cortex XDR?
Options
A After an endpoint group is created, its assigned security policy cannot be changed without deleting and recreating the group
B Endpoint groups are defined based on fields such as OS type, OS version, and network segment
C Each endpoint can belong to multiple groups simultaneously, allowing different security policies to be applied to the same device at the same time
D Endpoint groups require intervention to update the group with new endpoints when a new device is added to the network
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

5
Question
[Maintenance and Troubleshooting] An insider compromise investigation has been requested to provide evidence of an unauthorized removable drive being mounted on a company laptop. Cortex XDR agent is installed with default prevention agent settings profile and default extension "Device Configuration" profile. Where can an engineer find the evidence?
Options
A Check Host Inventory -> Mounts
B dataset = xdr_data | filter event_type = ENUM.MOUNT and event_sub_type =
ENUM.MOUNT_DRIVE_MOUNT
C preset = device_control
D The requested data requires additional configuration to be captured
Discussion (0 comments)

to join the discussion

Community Discussion

No discussions yet. Be the first to ask!

Finish Practice?

Are you sure you want to finish? This will end your practice session.